South Korea’s response to a personal-data breach at streaming platform Tving is raising broader questions about corporate accountability and the enforcement of cybersecurity rules, with potential implications for digital businesses operating in the country. CJ, Tving’s parent group, said it would consider support measures, including compensation for affected customers, as regulators face renewed calls to strengthen penalties for companies that obstruct data-breach investigations.
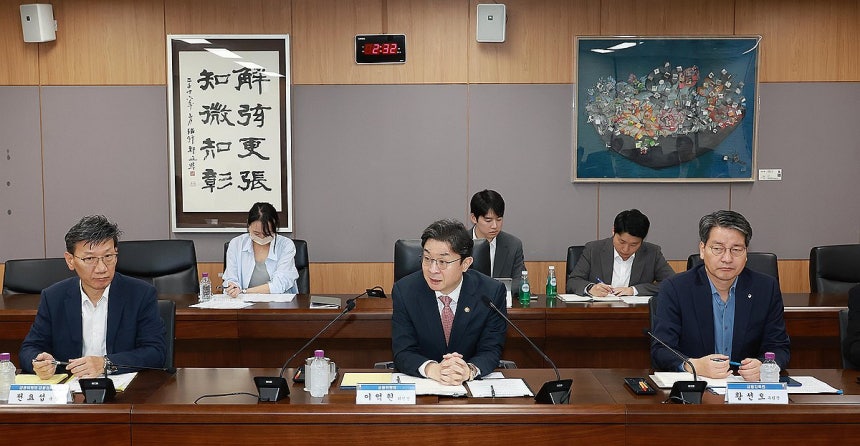
Han Min-soo, a lawmaker from the ruling Democratic Party of Korea, said on October 21 that CJ had formally conveyed its position during a National Assembly audit. Han had previously called for the conglomerate to take responsibility for the incident at Tving, which exposed information belonging to some users of CJ ONE, the group’s integrated membership service.
In a statement, CJ said that although Tving is directly responsible for operating the service and protecting personal information, the holding company recognizes its role in supporting data security standards that underpin customer trust.
The group said it viewed the exposure of information belonging to some CJ ONE members seriously and that protecting affected customers and preventing secondary harm were its immediate priorities. CJ added that it would consider support measures, including compensation, to address the incident and correct problems identified during the investigation and response.
Han urged the Personal Information Protection Commission, South Korea’s data-protection regulator, to closely monitor whether CJ follows through on its commitments. Commission Chair Song Kyung-hee said the agency would examine the matter carefully.
The parliamentary hearing also highlighted a separate regulatory concern: the difficulty of penalizing companies that conceal or destroy evidence before an official investigation begins.
Song said existing rules were insufficient to punish deliberate evidence concealment or destruction. While regulators consider whether companies cooperate promptly or obstruct investigations when calculating administrative fines, she said those factors alone do not provide an adequate deterrent.
Lawmaker Kang Jun-hyun called for legislation that would allow authorities to penalize companies that hide or destroy relevant records before a formal investigation starts. He argued that the current system risks disadvantaging organizations that report incidents properly while leaving others with limited exposure if they conceal evidence before investigators arrive.
Song said the commission suspected similar cases might exist beyond those in which authorities had obtained clear evidence warranting a criminal referral.
Previous investigations involving South Korean telecommunications companies KT and LG Uplus illustrate the issue. In KT’s case, regulators found that logs from 10 compromised servers had been deleted during a broader review that began in April 2025. The company initially said relevant records were unavailable, but later submitted separately retained materials after investigators identified signs of deletion. The commission decided to refer the case for prosecution over suspected obstruction.
LG Uplus was also found to have reinstalled operating systems on relevant servers or disposed of servers before the commission began investigating indications of a personal-data breach that surfaced through U.S. security publication Phrack in August 2025. Regulators said those actions made it harder to establish the precise circumstances of the breach and determine whether additional data had been exposed. The commission referred the matter to investigative authorities on suspicion of obstructing official duties.
The cases underscore the growing importance of evidence preservation as regulators confront cybersecurity incidents involving increasingly complex digital infrastructure. For streaming services, telecom operators and other data-driven businesses, the consequences of a breach can extend beyond technical remediation to compensation costs, regulatory scrutiny and reputational damage.
The debate in South Korea now centers not only on protecting customers after a breach, but also on ensuring that companies preserve the evidence needed to determine what happened and who should be held accountable.